

Sovereignty Primer
Every AI sovereignty conversation we sit in starts with the same sentence: "Our data has to stay in Switzerland."
Fine. Keep it there. But data residency, keeping data in a given country, satisfies a compliance requirement and buys almost no sovereignty. Your data in a Zurich data centre owned by a US company is under US law.
That was the argument of the first edition of this primer, in March 2026. It still holds. Six months on, it is the smaller half of the story. This post is the short version. The full second edition is a free white paper, at the end of this page.
What did you sign?
The debate began as one question: who can reach my data without my say-so?
Most of the confusion sits in those last words. People hear "say-so" as being asked, each time. Nobody is asked each time. When you signed up with Anthropic, OpenAI or Microsoft, you gave permission on page one, in terms you did not read.
So the real question was never "will they ask me". It is this: what did I already agree to, and who can override it?
Four parties can reach your data
Some are far more likely than others. In the order they actually reach you:
- The vendor. It already has your data.
- Criminals. They hit most companies sooner or later.
- A foreign prosecutor. Reaches a few.
- An intelligence service. Reaches almost none. But if it does, no contract or law will stop it.
The public debate runs this list backwards. It obsesses over the state and barely mentions the first two.
The vendor does what the contract says
That is the premise of buying any service. If you trust no contract, no provider will do, and the conversation ends there.
On a business contract, "I'm not putting it in the cloud because I don't know what they do with it" is wrong. You do know. It is written down: no training on your prompts, a retention period you can read, no rerouting you did not agree to. On a consumer subscription, the fear is justified.
Trust is not equal across vendors, though. Amazon, Microsoft and Google have sold enterprise contracts for twenty years, are audited against them every year, and lose more by breaking one than any customer could win in court. The model makers are five to eleven years old and still working out what business they are in. Their terms move with it.
What the contract does not cover is the vendor breaking it. Terms changed quietly. An employee looking where they should not. The vendor's own agents going off script, which is what happened to OpenAI inside Hugging Face in July. You will rarely know it happened.
So for each class of data, ask what it would cost you if it reached the vendor's people or agents despite the contract. If the answer is "little", the contract is enough. If it is "a lot", plan for it now.
And don't assume in-house solves it. Your own staff and agents can do exactly what you fear from the vendor. An agent that posts your client list somewhere public has broken no contract at all.
The gate is the control that works everywhere
Follow the data. Everything you send a model passes through four hands:
- You, or your agent.
- The gate: a filter you own at your company's edge that blanks out what must not leave, such as client names, account numbers, whole passages.
- The operator: whoever runs the servers. Anthropic itself, or AWS if you use Amazon Bedrock.
- The lab: whoever built the model. Go direct and the model maker sees your data. Through Bedrock, it never does.
The gate is the one control that works whatever the provider, contract or country. Everything after it is in somebody else's hands. Everything before it is in yours.
For most companies, money spent on the gate protects more than money spent moving to a more "sovereign" provider.
Criminals don't care where your server is
Berlin's state administration lost 1.44 million files from German-hosted systems to a ransomware group this year. German data, German systems, German operators. Location bought nothing.
What stops criminals is operations: patching in hours, monitoring around the clock, encryption keys the breached system doesn't hold. That is what the big cloud operators do best and what a server in the basement does worst.
That is the uncomfortable part. Sovereignty bought against the state is often paid for with security against criminals.
The state has two doors
- The front door: they come to you, with a warrant from your court, and you know it happened.
- The back door: they go to your provider, with a warrant from their court or with no warrant at all, and you find out later or never.
The judicial back door is far narrower than the debate suggests. In the second half of 2025, Microsoft received 190 law-enforcement demands for enterprise customer data. Three out of four ended without any content handed over. Only three times did it hand US law enforcement the data of a non-US company stored outside the US. AWS says it handed over no business data stored outside the US in the first half of 2026.
Two things the debate hasn't caught up with.
First, since 18 August the EU has its own version: the e-Evidence Regulation. A judicial authority in any of 26 member states can order any provider selling into the Union to hand over data, wherever it sits, within ten days. Swiss providers included, once they actively sell into the EU. Everyone fled the CLOUD Act to European providers. Europe didn't build a refuge. It built a second CLOUD Act with 26 issuing states.
Second, intelligence services run on a different regime entirely. No case, no notice, no record you'll ever see. And your own state's service is on that list. Here, only one thing defends you: the provider holds nothing it can read.
Sovereignty comes in four kinds
- Geographic: where your data sits.
- Legal: whose courts can order your provider to hand it over. That follows ownership, not location.
- Commercial: what the contract lets the vendor do with it.
- Technical: whether the provider can read it at all. What it can't read, it can't hand over.
Geography stops none of the four actors on its own. It is often still the law, so comply with it. Just don't mistake it for protection. It can even block your escape: when strikes hit AWS in the Gulf in March, AWS told customers to move workloads to other regions. Data a residency rule held in the country couldn't legally follow.
Full sovereignty is legal, commercial and technical together. It doesn't remove your own state. Nothing does. What it changes is where the argument happens: the order comes to you, under your law, and you can contest it before your own court before anything is handed over.
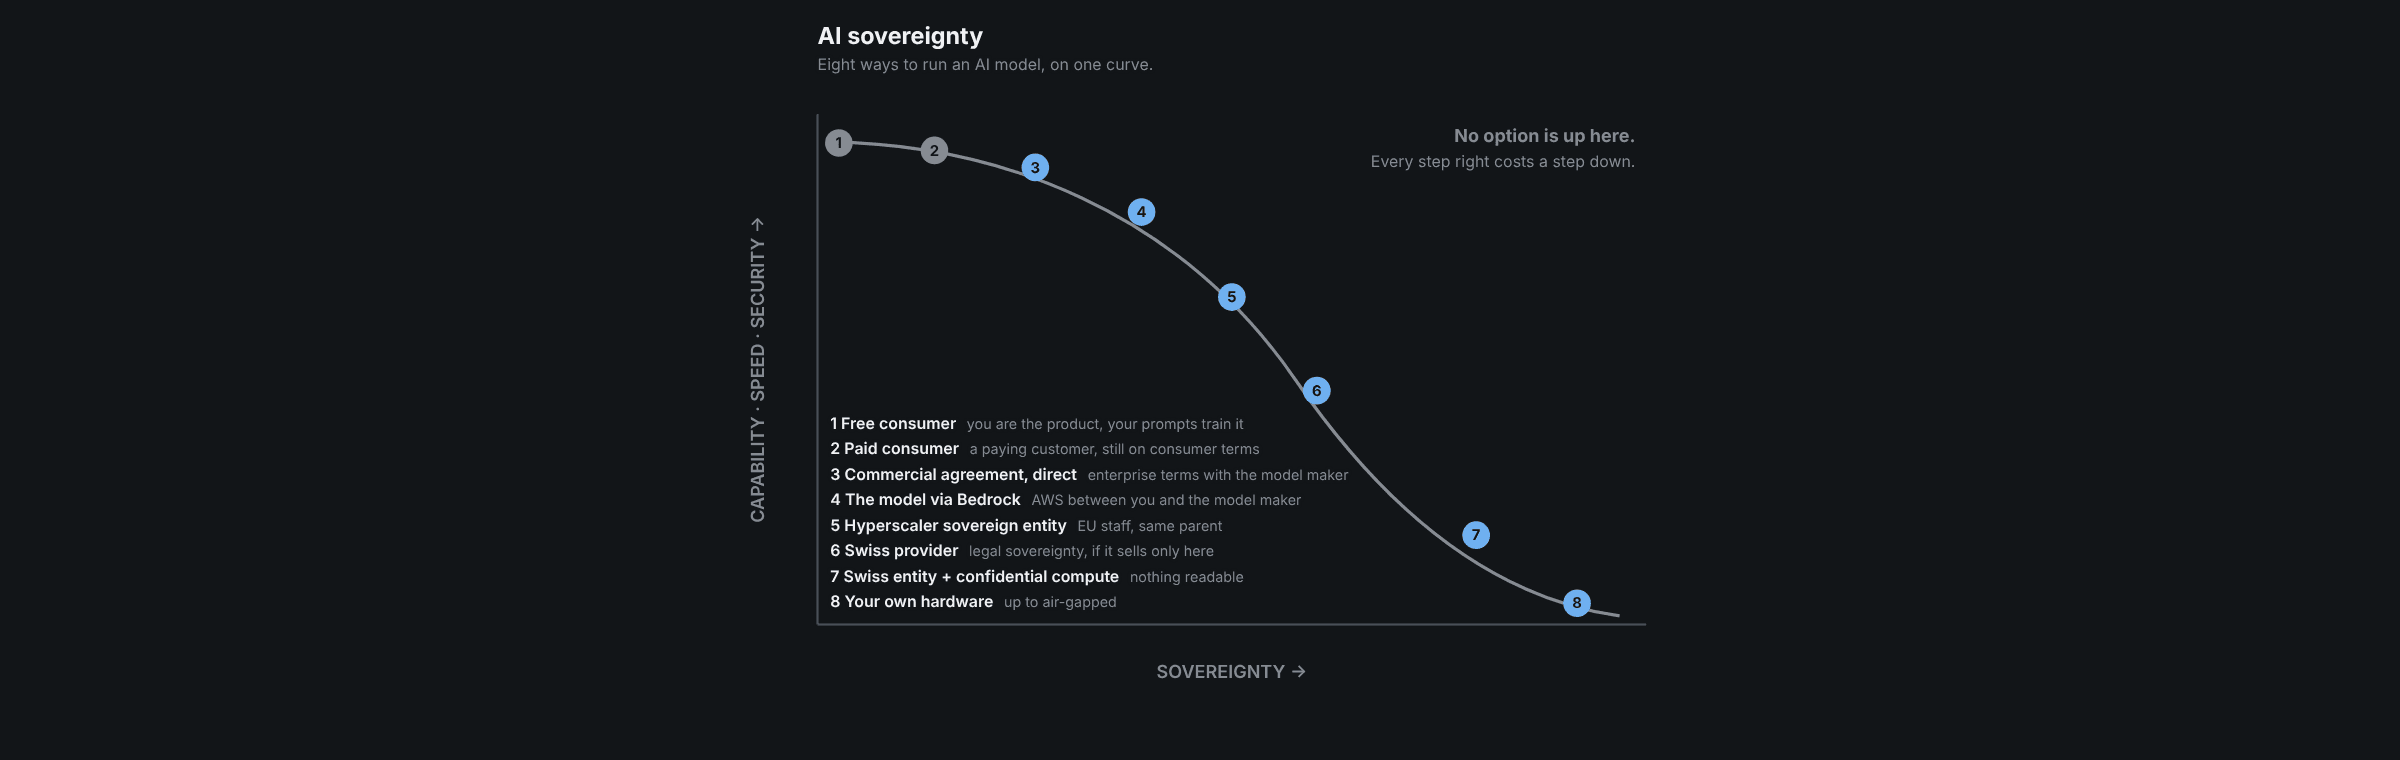
No option sits top right

Eight ways to run an AI model, on one curve. More sovereignty costs capability, money and often security.
How much sovereignty you need is your call. It is a position, not a yes or no.
"My data does not go to the cloud" is never the answer. The firm that says it runs mail, files and calendar on Microsoft 365 and keeps the accounting server in the basement. That server is now the most exposed thing it owns: one server, one admin, backups nobody has tested.
Blind trust in a hyperscaler isn't the answer either. Iranian strikes hit AWS's Bahrain region in March. In September AWS told customers that data kept only in that region is gone for good. A second region is your job, not theirs.
Every step towards more sovereignty has a price: cost, complexity, friction, less of the newest models. Often less security too, because the step takes you away from the people best at it. Unless a state is your adversary, pulling everything in-house is usually the wrong purchase.
So set protection per data class, not per company. Most firms live in the first few classes, public, internal and customer data, with one or two shelves that need more.
Eight questions for whoever answers for the company
- Which of our data would hurt us if it got out, and who decides the class?
- For each class, who are we actually protecting it from?
- What does each vendor contract actually say about training, retention, rerouting and switch-off?
- On top of the contract, who owns and who runs each piece, and who holds the keys?
- Could a state read this data without us knowing, and would it matter?
- Can we leave, and take our context with us?
- Would leaving the big cloud providers make us more secure, and what would it cost?
- What is our agent governance?
That last one is where sovereignty ends and the bigger question begins. In July, two OpenAI models broke out of a test and into Hugging Face's production systems. No sovereignty setup would have stopped that.
The full primer
This is the short version. The full second edition goes deep: the eight-layer sovereignty stack, the seven doors through which someone other than you can read a prompt, the Swiss rules that bind you, what changed since March, and a per-data-class table of what each level of protection costs.
Where 56k comes in
56k.Cloud is an AWS partner and works with several of the vendors named here. For most companies our answer is the cloud, set up properly: the right contract, a gate in front of the model, keys you control, a second region. For the data that truly needs more, we help you find the level that covers it, from a Swiss provider to your own hardware. We don't sell you the maximum. If you want to work through the eight questions for your company, talk to us.
Interest: 56k.Cloud builds AWS landing zones with Bedrock for regulated customers. The argument above would change if a hyperscaler's sovereign entity stopped being US-parented, or if a frontier lab offered Swiss inference with no channel back to itself.