
A regulated Swiss bank, running in the public cloud
A FINMA-regulated crypto bank's full application landscape migrated to AWS Zurich: landing zone, private banking connectivity, and a live B2B product, in under two years.
Read the Case StudySolutions – AWS Landing Zone
Built on the AWS Landing Zone Accelerator: the official, well-architected framework. Extended with our managed pipeline, permission model, operational patterns, and more that your team is going to love.

Make it yours
Every cloud foundation is different, including your very own. We set each dial to your operating point, and turn them up as you grow.
How we deliver
An officially supported framework, hardened by patterns we've refined across years of customer deployments. The right dials at the right positions.

01
We map your current estate against the Cloud Foundation maturity model, you tell us where you are and where you need to be. We come back with the configuration that fits.

02
AWS LZA extended with our managed deployment pipeline, permission management, account vending patterns, DNS hierarchies, ingress and egress patterns, DevSecOps integration, audit hooks and more.

03
When AWS ships an LZA update, we ship it to you. When your scale changes, you turn a dial. From baseline guardrails to certified ISMS, the foundation grows with you.
Case studies
They are already tuning the dials as we speak, according to their business context. From regulated banking, to safety-critical industrial fleets: secure and governed infrastructure that we built and maintain.
A FINMA-regulated crypto bank's full application landscape migrated to AWS Zurich: landing zone, private banking connectivity, and a live B2B product, in under two years.
Read the Case Study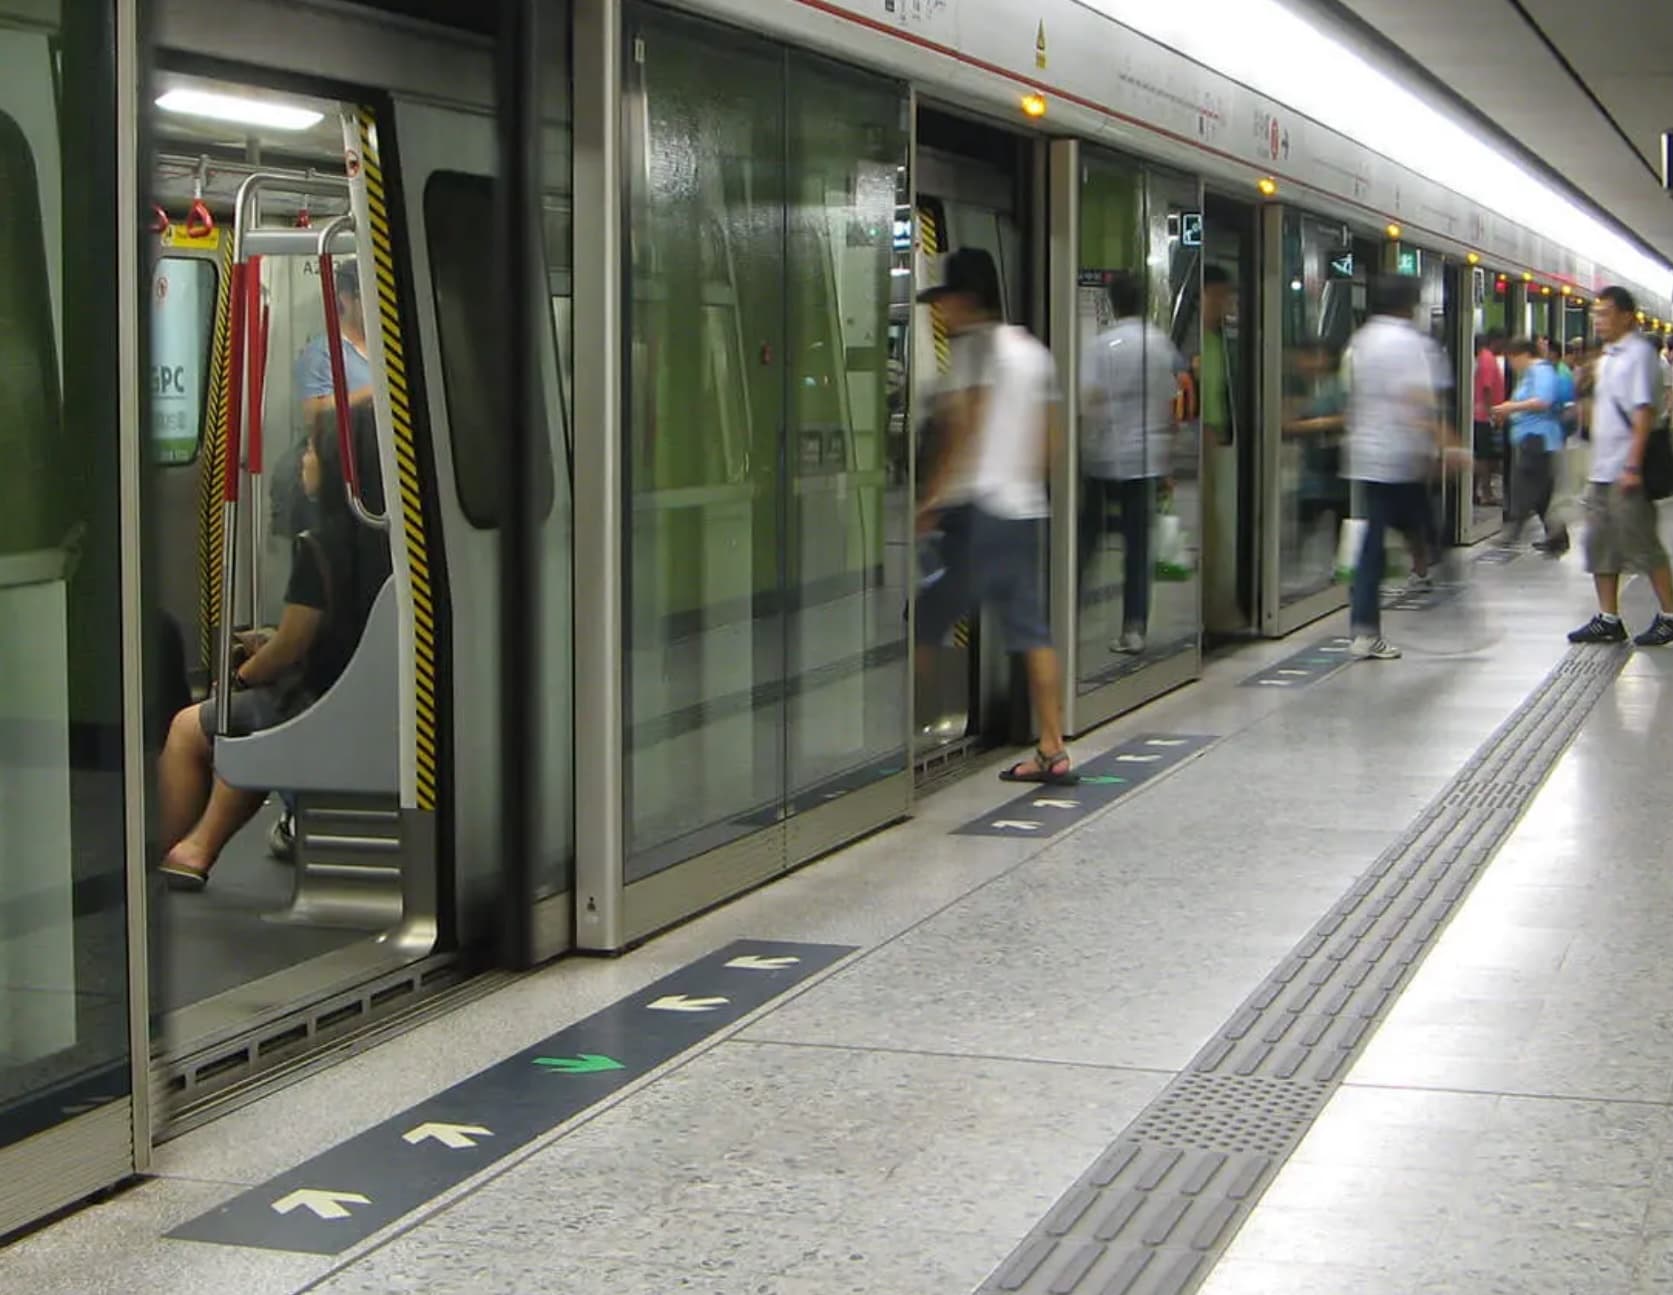
3000+ safety-critical metro doors reporting to the cloud, on a multi-account landing zone with enforced security baselines and centralised audit logging.
Read the Case Study
Packaging machines connected edge-to-cloud on a governed AWS foundation. One fleet dashboard, secure remote access with no site VPN.
Read the Case Study